Establish a future-ready control plane for digital trust. As certificate lifespans collapse and quantum threats accelerate, discover how to automate trust natively through your network.
The foundation of digital trust is shifting as organizations face simultaneous pressures from shorter lifespans and quantum threats, now accelerated by the unprecedented power of Frontier AI.
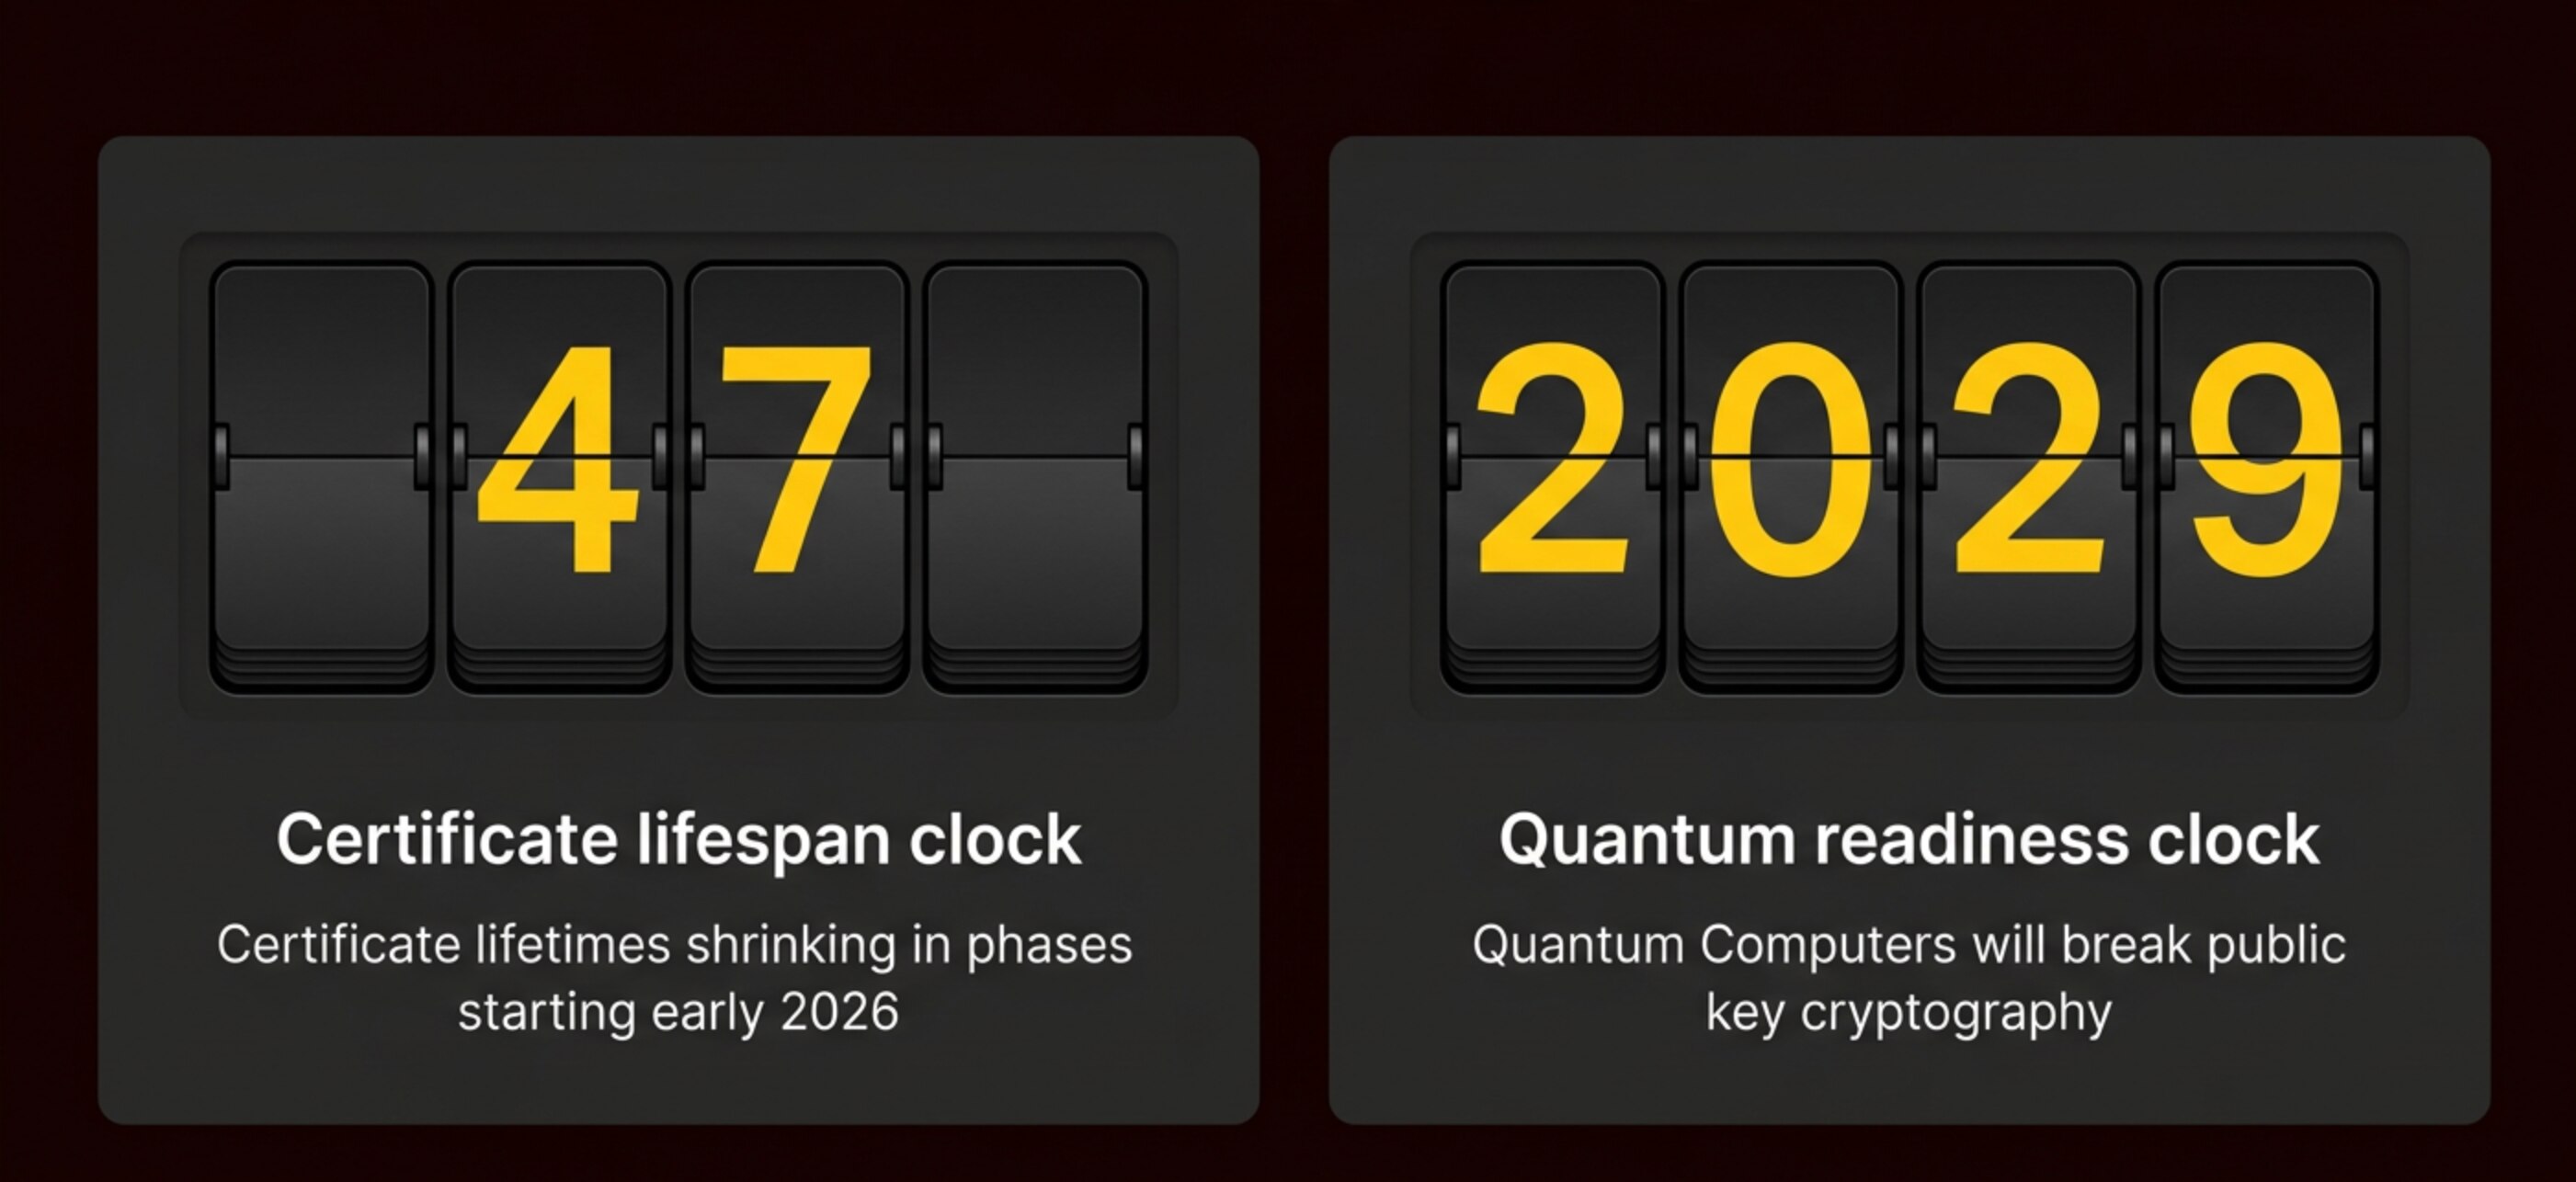
Trust Clock
Trust Clock
Certificate lifespans are shrinking to 90 days or less, making manual management a primary cause of avoidable outages.
The Quantum Clock
The Quantum Clock
"Harvest Now, Decrypt Later" (HNDL) attacks mean data with a 2029+ shelf life is already vulnerable today.
The network provides the only strategic vantage point for Posture, Enforcement, and Operations. Leverage your existing security fabric to automate trust and upgrade to quantum-safe standards.
Modernize your infrastructure to handle shorter certificate lifecycles and cryptographic AI and PQC threats.
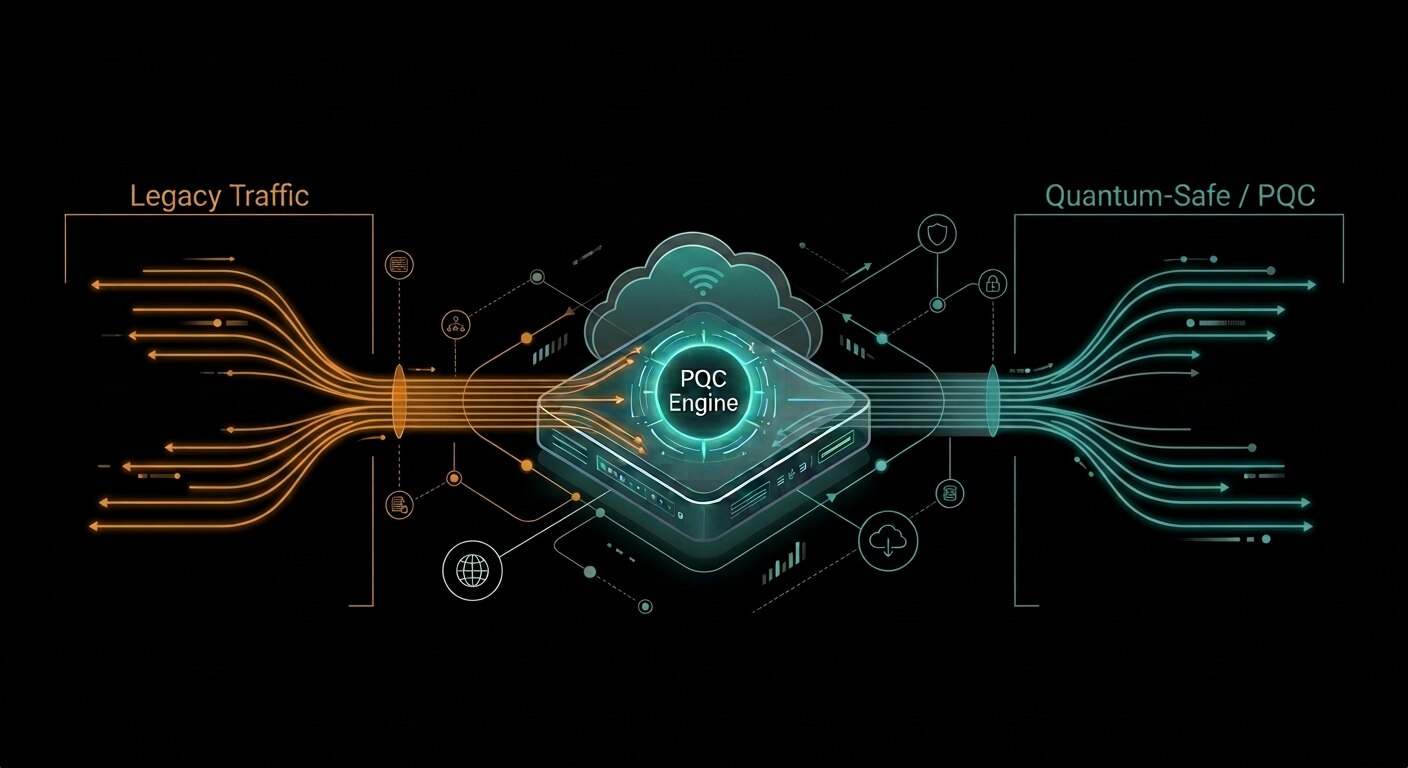
Upgrade cryptography without changing applications
Translate legacy traffic to quantum-safe standards at the edge. Extend crypto-agility to IoT, OT, and mainframe systems.
Discover managed and unmanaged certificates and automate renewal to save 48 hours of manual labor per certificate every year.
Discover certificates and automate issuance, renewal and replacement across the environment. Reduce outages and manual work as certificate lifespans continue to shrink.
Maintain a continuously updated inventory of all cryptographic assets and protocols.
Use network-derived visibility to identify certificates, protocols, algorithms and dependencies. Map them to applications and prioritize cryptographic risk without host agents.
Modernize PKI for greater scale and resilience
Modernize legacy PKI with automated certificate issuance and consistent policy enforcement. Standardize trust, strengthen resilience and scale private PKI across diverse environments.
Keep software trusted with secure code signing
Automate signing workflows, secure keys in encrypted storage and enforce role-based policies. Give teams visibility and control while allowing developers to move quickly.
Secure machine identities across Kubernetes environments
Discover and control TLS, mTLS and SPIFFE identities across cloud-native, multicloud and multicluster environments. Standardize cert-manager policies to improve reliability and reduce DevOps effort.
INSIGHTS
Turn Cryptographic Debt into Business Resilience
Reduce operational risk, prevent disruption and give teams the visibility, automation and control to modernize cryptography at their own pace.
Operational Efficiency
Automate repetitive certificate and cryptographic tasks to reduce manual work, improve consistency and give security teams time back.
Business Continuity
Prevent certificate-related outages and modernize cryptography without forcing disruptive changes to applications or infrastructure.
Compliance Readiness
Maintain visibility, policy enforcement and audit-ready reporting to support NIST, CNSA 2.0 and internal cryptographic requirements.
Faster Risk Reduction
Identify exposed applications, weak algorithms and certificate risks. Then prioritize remediation based on business impact.
Frequently Asked Questions
Frequently Asked Questions About the Cryptographic Reset
The cryptographic reset is the move from static, manually managed cryptography to continuous visibility, automation and control. It's being driven by shrinking certificate lifespans, AI-assisted cryptanalysis, quantum risk, expanding machine identities and evolving standards.
Attackers can collect encrypted data today for future decryption, while certificate lifespans are shrinking and AI is accelerating cryptographic research. Because discovery and migration can take years, organizations need to start building visibility and a phased roadmap now.
Cryptographic agility is the ability to replace or upgrade algorithms, keys, certificates and protocols without redesigning systems or disrupting operations. It allows organizations to respond as standards, threats and certificate requirements change.
Quantum-Safe Security uses existing network telemetry and ecosystem data to identify cryptographic usage, map dependencies and build a continuously updated CBOM. Teams can then prioritize vulnerable assets and remediation using exposure and business context.
Next-Generation Trust Security discovers certificates and automates renewal, provisioning and policy enforcement. This reduces manual effort and lowers service-interruption risk as certificate volumes grow and renewal cycles accelerate.
For supported TLS 1.3 use cases, PAN-OS® 12.1 firewalls can translate between classical and post-quantum encryption. This helps protect legacy and modern applications without requiring immediate application rewrites.
Requirements depend on the capability, PAN-OS version, traffic volume and performance needs. Some quantum-security functions run on supported existing firewalls, while high-scale PQC decryption and inspection may benefit from quantum-optimized hardware.
NGTS brings these functions together with network visibility and enforcement. CLM manages certificate discovery, issuance, renewal, deployment and retirement. PKI provides the trust infrastructure for issuing and validating certificates.
Yes. Machine identity security can extend to code-signing operations and Kubernetes environments. This includes centralized control of signing keys and activity, plus discovery and policy for TLS, mTLS, SPIFFE and cert-manager across clusters.
Start with ownership and discovery. Build an inventory of cryptographic assets and dependencies, classify them by business impact and data sensitivity, and then prioritize certificate automation and migration to hybrid and post-quantum cryptography.